
 Контакт
 Как се пазарува?

Доставка
Наръчник за пазаруване
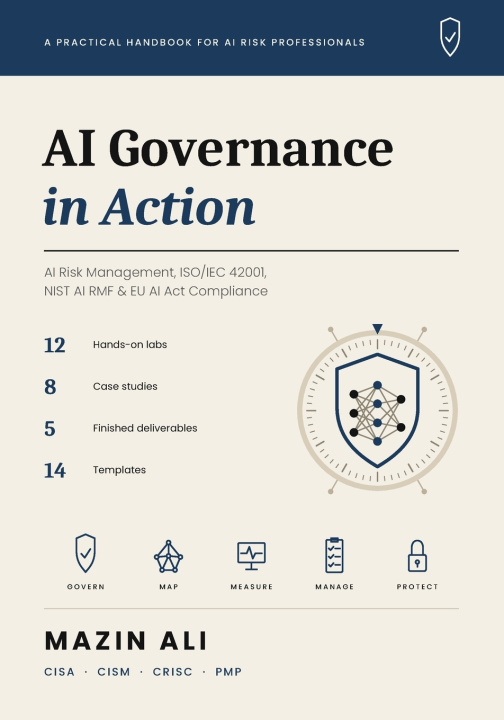
AI Governance in Action
A Practical Handbook for AI Risk Management, ISO/IEC 42001, NIST AI RMF, and EU AI Act Compliance
 Английски език
 36 b
 Подготвяме
 Нови
До 30 дни за връщане на стоки

Learn to govern AI the way it is actually done in organizations, explained in plain English, with hands-on labs and finished professional deliverables.
AI is now in the chatbot that answers customers, the tool that screens job applicants, and the model that flags fraud. Someone has to know what AI is in use, who owns it, what could go wrong, which laws apply, and how to prove it is under control. This book shows you how, step by step. No coding required.
One fictional company runs through every chapter, so the AI system you inventory is the one you assess, control, secure, monitor, and audit.
Written by a cybersecurity governance, risk, and compliance professional who holds the CISA, CISM, CRISC, CompTIA Security+, CompTIA CySA+, and PMP certifications, and author of Cybersecurity GRC in Action.
Inside you'll find:
- 12 hands-on labs: build an AI inventory, sort systems by risk, run a risk and impact assessment, write a model card, threat-model a chatbot, plan an AI audit, and more
- 8 case studies across banking, healthcare, retail, staffing, software, manufacturing, government, and professional services
- 5 finished deliverables: an AI acceptable use policy, an AI risk and impact assessment, a model card, a vendor AI review, and an AI audit report
- 14 templates, 22 exercises with answer keys, and a one-page AI pre-approval checklist
- Interview questions with model answers for AI governance roles
Topics covered:
NIST AI Risk Management Framework and Generative AI Profile · ISO/IEC 42001 and related standards · EU AI Act, including the 2026 amendments and new deadlines · U.S. federal and state AI laws · insurance AI rules · AI inventory and risk tiering · fairness testing explained simply · AI security, prompt injection, and the OWASP Top 10 for LLMs · third-party and generative AI tools · monitoring, incidents, and AI audit · careers in AI governance
Perfect for:
- Risk, compliance, audit, privacy, and security professionals given responsibility for AI
- Managers who own AI systems
- Anyone starting a career in AI governance
Current as of 2026.
Scroll up and get your copy today.


Информация за книгата
Английски език

Подарете тази книга днес
Лесно е
1 Добавете книгата в количката си и изберете Доставка като подарък 2 В замяна ще ви изпратим ваучер 3 Книгата ще пристигне на адреса на получателяЗдравейте! Аз съм Libroamiko, вашият книжен съветник.
Как мога да ви помогна?